Ethical Hacking
Ethical Hacking Services in Miami: A Legal Guide for Businesses (2026)
Learn how legal ethical hacking services help Miami businesses find exploitable security gaps, what written authorization must cover, which tests to request, and how to hire a legitimate provider.
Ethical hacking services give a business permission-based evidence about how an attacker could reach its systems, data, or operations. A qualified tester uses adversarial techniques, but does so under a contract, within a defined scope, and with safeguards designed to prevent disruption. For Miami organizations facing fraud, ransomware, cloud exposure, account takeover, and vendor risk, that distinction between authorized testing and illegal access is essential.
This guide explains what legal ethical hacking looks like in practice, the tests Miami businesses can request, the documents that should exist before testing begins, and how to choose a provider. It is general security information, not legal advice; counsel should review unusual, high-risk, or multi-party engagements.
What are ethical hacking services?
Ethical hacking is authorized security testing performed to identify and safely validate weaknesses before criminals exploit them. It is often used as an umbrella term for penetration testing, red teaming, application security testing, cloud security testing, wireless testing, and carefully controlled social-engineering assessments.
The word ethical does not come from a tool or certification. It comes from permission, purpose, limits, and professional conduct. The tester must have written authorization from someone who has the legal authority to grant it. The work must stay inside the named systems, dates, methods, and objectives. Findings must be handled confidentially and reported to the client rather than used for personal benefit.
When is ethical hacking legal?
In the United States, accessing a computer or account without authorization can create serious civil and criminal exposure under laws including the federal Computer Fraud and Abuse Act. Florida also addresses unauthorized computer access and related conduct in Chapter 815 of the Florida Statutes. A client's verbal request or ownership of a company name is not enough for a careful provider; authority and scope should be documented before access begins.
"No written authorization, no test. A legitimate ethical hacker protects the client, affected third parties, and the testing team before touching a system."— Cybrvault operating principle
A proper authorization package normally includes a signed statement of work and rules of engagement. If a cloud platform, managed provider, payment environment, landlord-controlled network, franchise system, or other third party owns part of the target, the client may also need that party's approval. Responsible testers verify this instead of assuming permission transfers automatically.
Written authorization should identify
- The legal client entity and the person authorized to approve testing.
- Exact in-scope domains, applications, IP addresses, cloud accounts, offices, wireless networks, and user groups.
- Explicit exclusions, such as life-safety systems, production databases, payment processing, destructive actions, or denial-of-service testing.
- Permitted methods, testing dates and hours, source IP addresses, and geographic limitations.
- Emergency contacts, stop-work authority, escalation steps, and what happens if an active compromise is discovered.
- Rules for collecting, encrypting, retaining, sharing, and securely destroying evidence.
- Third-party approvals and provider notification requirements when applicable.
Legal ethical hacking versus illegal hacking
- Legal: testing a company's web application after its authorized executive signs a scope naming that application and the approved techniques.
- Legal: conducting a controlled phishing simulation against employees when leadership has authorized the campaign and safety rules protect participants.
- Not authorized: entering a spouse's, employee's, competitor's, tenant's, or former partner's email, phone, cloud account, or social profile without the account owner's lawful consent.
- Not authorized: targeting a third-party vendor merely because it exchanges data with the client.
- Not authorized: continuing after the testing window ends, crossing an excluded boundary, retaining unnecessary personal data, or using a finding for leverage.
Searches such as “hire a hacker” or “recover an account by hacking it back” often lead to scams and unlawful offers. A legitimate Miami ethical hacking company will verify ownership, refuse revenge or surveillance requests, explain what it can lawfully test, and recommend account-recovery, legal, or investigative channels when offensive testing is inappropriate.
Ethical hacking services Miami businesses can request
1. External network penetration testing
The tester evaluates approved internet-facing assets such as firewalls, VPN gateways, remote-access portals, mail infrastructure, and exposed services. The goal is to determine whether an outsider could gain an initial foothold, not simply to list software versions. This is a common starting point for professional firms, healthcare practices, hospitality groups, financial businesses, and property companies across Miami-Dade.
2. Web application and API testing
A human-led test examines authentication, authorization, session handling, data exposure, file uploads, payment or business workflows, and API behavior. Testers look for weaknesses such as users reaching another customer's records, changing protected values, bypassing intended approval steps, or exposing secrets. This is materially different from a basic website malware scan.
3. Internal network testing
An internal assessment asks what could happen after a laptop, employee account, office port, or remote session is compromised. Testing can cover segmentation, identity permissions, sensitive file access, administrative pathways, and whether one limited account can reach critical systems. High-risk actions should be simulated or separately approved rather than assumed.
4. Cloud security testing
Cloud testing evaluates approved AWS, Azure, Google Cloud, Microsoft 365, Google Workspace, and software-as-a-service configurations. Common objectives include finding excessive privileges, public data exposure, weak identity controls, unsafe secrets, insecure integrations, and paths between cloud services. The provider's testing policy and the client's subscription responsibilities must be checked during scoping.
5. Wireless and on-site testing
For Miami offices, hotels, clinics, warehouses, marinas, and multi-tenant buildings, wireless testing can validate whether guest networks are isolated, corporate Wi-Fi resists impersonation, and nearby signals expose unintended access. Physical access testing may be added only with precise boundaries, site contacts, safety restrictions, and procedures for security personnel.
6. Social-engineering assessments
Approved phishing, phone-pretexting, or access-control exercises measure how people and procedures respond to realistic pressure. Ethical campaigns avoid humiliating staff, collecting unnecessary credentials, or creating unsafe situations. Results should improve verification processes and training, not rank or punish individuals.
7. Red team exercises
A red team pursues an agreed business objective across multiple approved paths while defenders test detection and response. This is best for organizations with mature monitoring and incident procedures. Businesses still fixing basic vulnerabilities usually gain more from a focused Miami penetration test first.
What a professional engagement looks like
- 1Discovery and ownership verification. The provider identifies the business objective, system owners, dependencies, sensitive data, and any third parties whose consent may be required.
- 2Scope and rules of engagement. Both parties document targets, exclusions, testing windows, approved techniques, emergency contacts, evidence rules, and stop conditions.
- 3Threat-informed reconnaissance. Testers map the approved attack surface and likely paths using public information and client-provided context without crossing the agreed boundary.
- 4Controlled testing. Automated tools support coverage, while human testers validate findings, examine business logic, and avoid unnecessary operational risk.
- 5Immediate escalation. A critical exposure or evidence of an active intruder is reported through the agreed emergency channel rather than held for the final presentation.
- 6Reporting. Leadership receives a concise business summary; technical teams receive verified evidence, affected assets, risk reasoning, and practical remediation guidance.
- 7Remediation and retesting. The client fixes prioritized issues and the tester validates that the original attack path is closed without creating a new weakness.
What should be in the final report?
The report is the lasting value of the engagement. It should state what was and was not tested, summarize the methods used, distinguish verified exploitation from scanner observations, and connect technical weaknesses to business outcomes. Each finding should name the affected asset, include enough sanitized evidence to support the conclusion, explain likelihood and impact, and provide specific remediation steps.
- An executive summary written for owners, leadership, counsel, and risk stakeholders.
- A scope statement, limitations, testing dates, and methodology.
- Prioritized findings based on exploitability and business impact—not severity labels alone.
- Evidence handled so passwords, tokens, customer records, and unnecessary personal information are not exposed.
- Clear remediation ownership and a practical order of operations.
- A retest result showing which findings were fixed, remain open, or need compensating controls.
How to choose an ethical hacking company in Miami
Choose for fit and discipline rather than theatrical branding. The best provider for a web application may not be the best choice for wireless, cloud, or physical testing. Ask who will perform the work, whether those people have relevant hands-on experience, and how the proposed effort maps to your actual risk.
- 1Ask for a redacted sample report. Look for clear evidence, business context, and useful remediation—not pages of scanner output.
- 2Confirm the named testers and their experience with your technology and industry. Certifications can support credibility, but they do not replace relevant work samples and references.
- 3Ask how much testing is manual. Automation helps with breadth; people are needed to validate, chain, and contextualize weaknesses.
- 4Review the rules of engagement before signing. If a provider treats authorization, stop conditions, and data handling as paperwork to finish later, do not proceed.
- 5Confirm confidentiality, secure evidence transfer, retention periods, deletion, insurance, and subcontractor disclosure.
- 6Require a remediation meeting and retest terms. A report without a path to closure leaves the business with a list rather than a result.
- 7Check local availability when the scope includes a Miami office, wireless environment, urgent validation, or an executive briefing.
Warning signs of a fake or unsafe hacker-for-hire offer
- They promise access to any phone, email, social account, bank account, or messaging service without verifying ownership.
- They ask for cryptocurrency, gift cards, or full payment through an untraceable channel before defining a scope.
- They claim guaranteed access or guaranteed recovery. Ethical testers cannot promise a vulnerability exists.
- They refuse a contract, identity verification, references, a business address, or a secure way to exchange evidence.
- They propose installing spyware, impersonating law enforcement, targeting family members, or accessing third-party systems.
- They offer to erase records, change grades, alter debts, retrieve private messages, or retaliate against someone.
If your real need is to recover a hacked account, preserve evidence, investigate fraud, or remove exposed personal data, say that during the first call. The lawful solution may be incident response, digital forensics, OSINT, platform recovery, or legal process—not hacking. Cybrvault's OSINT investigations guide explains one non-intrusive investigative path.
Why local context matters in South Florida
Miami organizations combine international customers, multilingual teams, luxury real estate, hospitality, healthcare, legal services, finance, logistics, marine operations, seasonal properties, and a large remote workforce. That mix creates unusual identity, payment, vendor, wireless, and physical-access risks. A well-scoped assessment should reflect how the business operates—not repeat the same checklist for every client.
Local work can also matter when testing must occur on-site, leadership wants an in-person briefing, a property has multiple network owners, or hurricane preparations and recovery procedures affect the testing window. Cybrvault serves Miami, Miami Beach, Brickell, Coral Gables, Coconut Grove, Doral, Aventura, Kendall, Pinecrest, Fort Lauderdale, Broward County, and businesses throughout South Florida.
A practical ethical-hacking readiness checklist
- 1Name the business decision the test must support: reduce breach risk, validate a new application, satisfy a customer request, test monitoring, or verify remediation.
- 2List the systems you own and identify systems controlled by cloud providers, landlords, franchises, vendors, or customers.
- 3Choose a focused first scope rather than authorizing everything at once.
- 4Identify operational blackouts, fragile systems, sensitive data, backup owners, and emergency contacts.
- 5Collect architecture diagrams, test accounts, prior reports, and known risks so tester time is spent on meaningful validation.
- 6Assign owners who can fix application, identity, cloud, network, and process findings after the report arrives.
- 7Schedule the remediation review and retest before the engagement begins.
Cybrvault services for Miami and South Florida
Cybrvault provides permission-based offensive security and related protection services for organizations and individuals across South Florida. Every ethical hacking engagement begins with ownership verification, a written scope, and agreed safety boundaries.
- Ethical Hacking — authorized web, API, mobile, network, cloud, wireless, social-engineering, and red-team assessments.
- Miami Ethical Hacking — local penetration testing and offensive-security support for Miami-Dade organizations.
- Cybersecurity — risk assessments, hardening, incident planning, and security improvement programs.
- 24/7 Monitoring — continuous detection, triage, threat hunting, and response support.
- OSINT — lawful digital-footprint, breach-exposure, due-diligence, and threat-intelligence research.
- Personal Security — private digital protection for executives, families, residences, and personal devices.
Request a legal ethical hacking assessment
If you own or are authorized to represent the systems you want tested, contact Cybrvault for a confidential scoping conversation. We will help identify the correct test, document the boundaries, and build a practical engagement around your Miami or South Florida environment. We do not accept requests to access third-party accounts or systems without lawful written authorization.
// frequently asked
Questions teams ask us
Are ethical hacking services legal in Miami, Florida?+
Yes, when testing is expressly authorized by the lawful system owner and remains within a written scope. The agreement should identify targets, dates, allowed methods, exclusions, emergency contacts, and evidence-handling rules. Accessing an account or system without authorization can violate federal and Florida law.
What is the difference between ethical hacking and penetration testing?+
Ethical hacking is the broader permission-based practice. Penetration testing is a defined engagement in which testers identify and safely validate exploitable weaknesses within an agreed scope. Red teaming, application testing, cloud testing, and approved social engineering can all fall under ethical hacking services.
Can I hire an ethical hacker to access someone else's phone or account?+
No legitimate provider should access another person's phone, email, social profile, cloud account, or financial account without lawful authorization from the owner. Account recovery, fraud, harassment, and evidence matters should use platform recovery, incident response, legal counsel, law enforcement, or a properly licensed investigation route as appropriate.
What should I provide before a Miami penetration test?+
Prepare proof of ownership or authority, a list of proposed systems, business objectives, third-party dependencies, sensitive-data concerns, testing blackout periods, technical and executive contacts, prior reports, and the people responsible for remediation. The provider should convert this into a written scope and rules of engagement.
Will ethical hacking disrupt business operations?+
Professional testing is designed to manage operational risk, but no meaningful security test is entirely risk-free. The rules of engagement should exclude destructive techniques by default, identify fragile systems, define testing windows and stop conditions, and maintain an immediate communication channel. Higher-risk actions require separate explicit approval.
Does Cybrvault provide ethical hacking services outside Miami?+
Yes. Cybrvault supports authorized remote engagements and serves Miami-Dade, Broward, Palm Beach, the Florida Keys, and organizations elsewhere by arrangement. On-site availability depends on the scope, property authorization, and scheduling requirements.
// miami, fl services
Cybersecurity built for South Florida
// need help applying this?
Book a free, confidential consultation.
Our engineers can map this to your environment in 30 minutes.
Get secured// keep reading
Related articles
Ethical Hacking
Penetration Testing in Miami: The 2026 Buyer's Guide for Businesses & Ethical Hacking Teams
A local, no-fluff guide to penetration testing in Miami — what a real pentest looks like in 2026, how ethical hackers scope engagements, pricing, FIPA and HIPAA fit, and the questions that separate a real Miami pen test from a Nessus scan with a logo.
Ethical Hacking
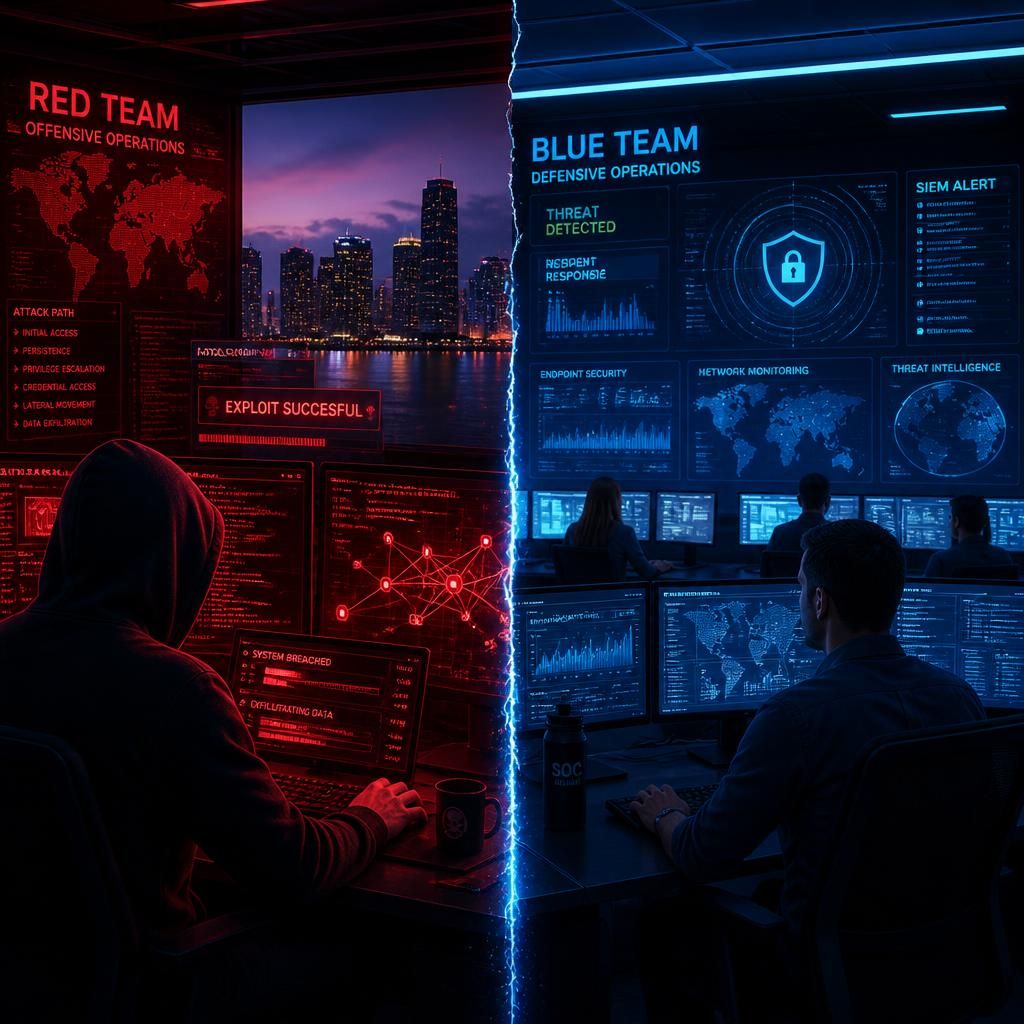
Red Team vs Blue Team in Cybersecurity: The 2026 Guide for Miami Businesses
Red team vs blue team — what each side actually does, how they work together (purple teaming), and how Miami businesses use both to stress-test defenses in 2026. Real engagement examples, pricing, FIPA/HIPAA fit, and how to know which one you need first.
Home Security
Home Network Security in 2026: How South Florida Homeowners Can Protect Their Homes From Cyber Attacks
A complete home network security guide for South Florida homeowners: how hackers get into home Wi-Fi, cameras, and smart devices, the exact settings to change today, hurricane-season considerations, and a weekend hardening checklist.